Secure your data with technology

Get Your Organization

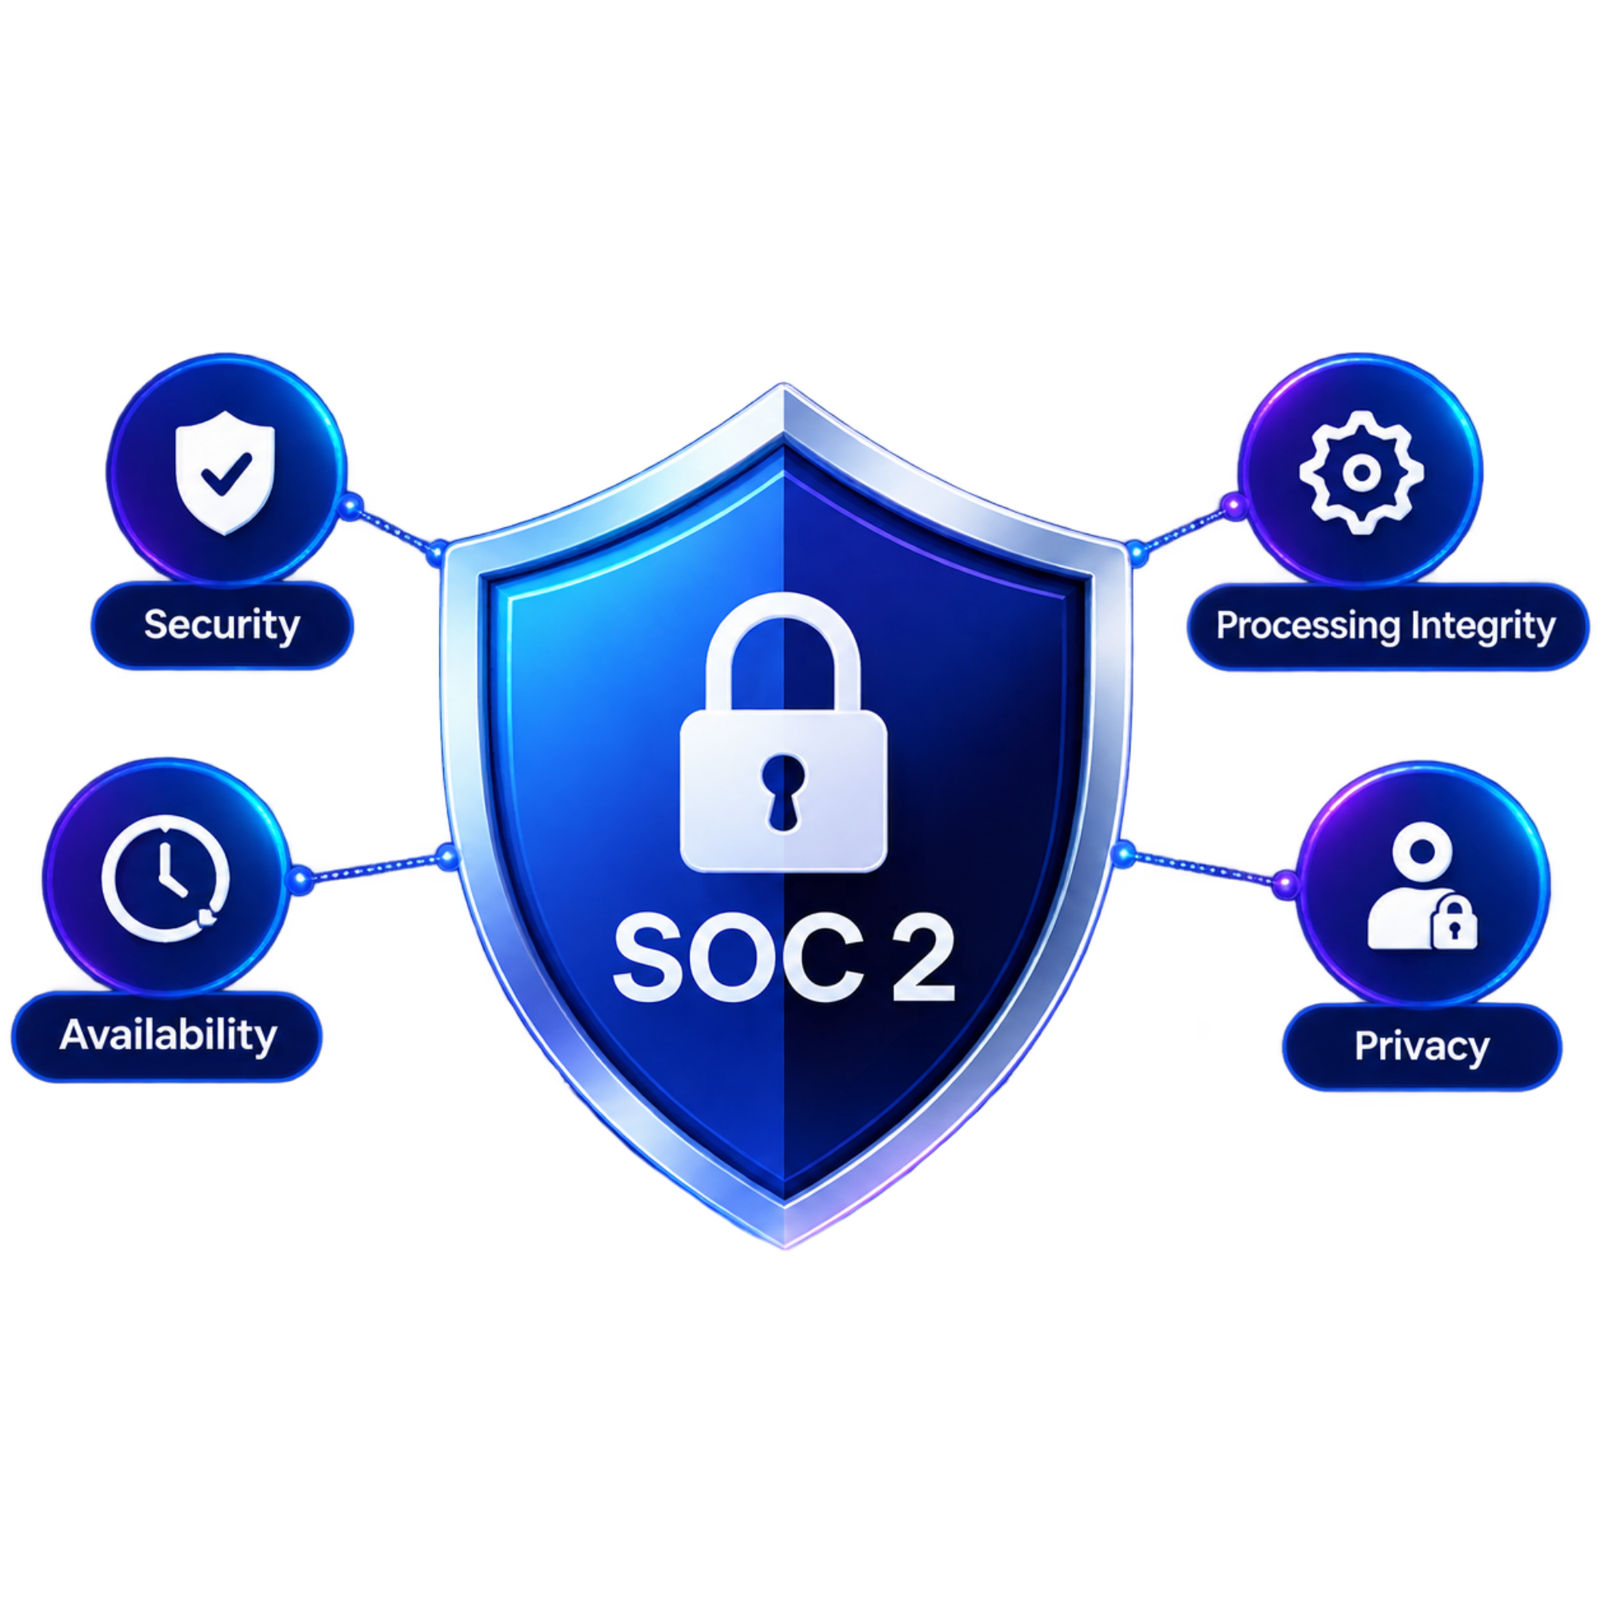
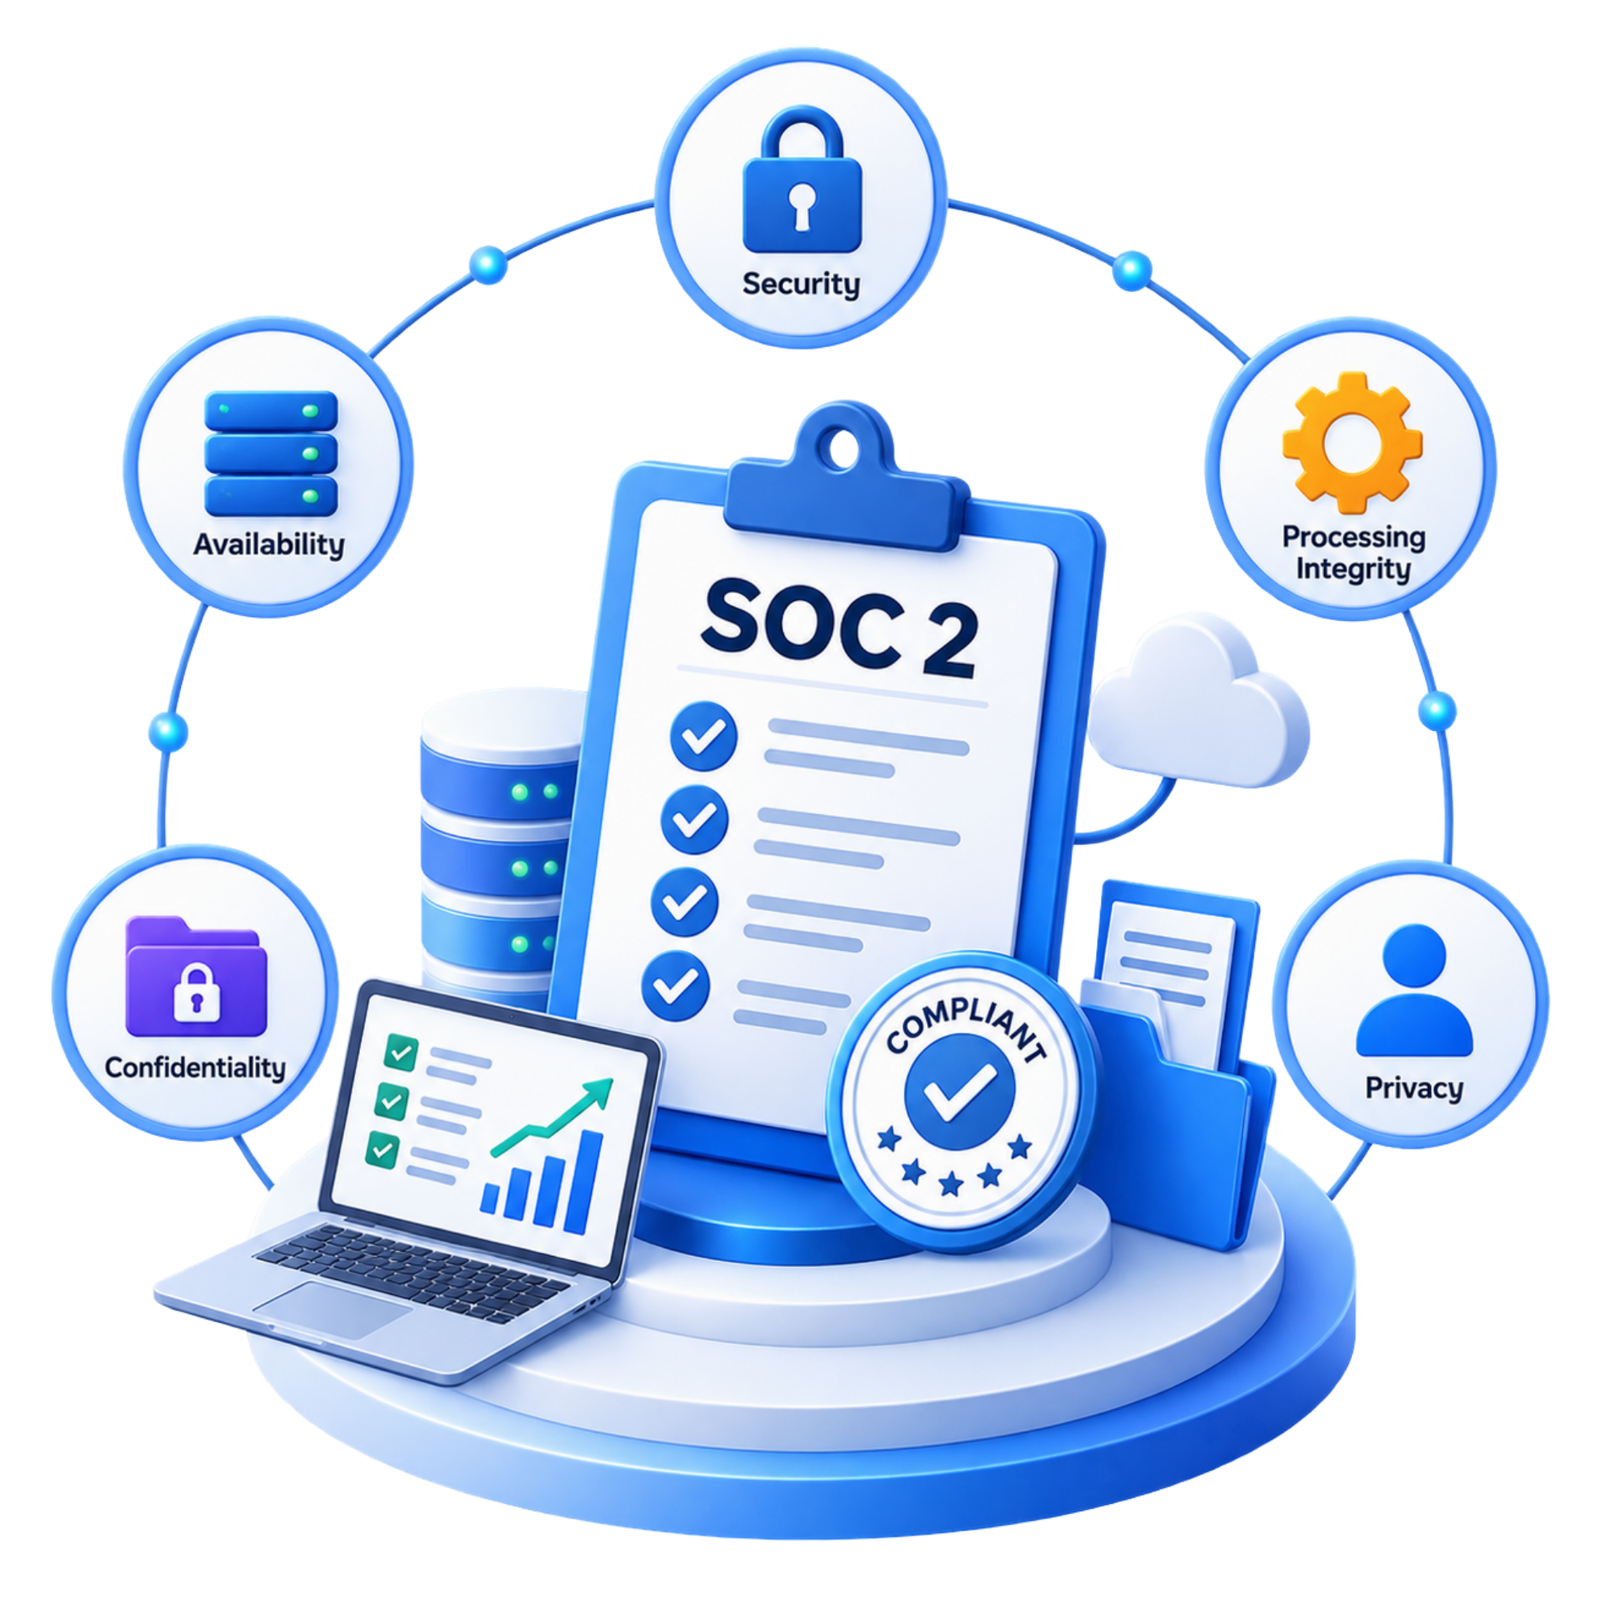
SOC 2 or Service Organization Control 2 is a framework designed to assess and ensure the security, availability, processing integrity, confidentiality, and privacy of data within technology and cloud computing organizations.

Developed by the American Institute of CPAs (AICPA), SOC 2 is part of the broader System and Organization Controls (SOC) framework, which defines criteria for managing and securing sensitive information.

WHY SOC 2 MATTERS?

Features and Benefits of soc 2

SOC 2 specifically focuses on the

controls and processes related to the security, availability, processing integrity, confidentiality, and privacy of data stored in the cloud. It is often used by technology and cloud service providers to demonstrate their commitment to protecting client data.

Enhanced Security Measures

Strengthen your security controls and protect sensitive information with reliable compliance practices.

Increased Trust & Credibility

Demonstrate your commitment to security and compliance, building greater trust with clients and stakeholders.

Efficient Risk Management

Identify potential risks, strengthen internal controls, and implement effective measures to reduce security threats.

Client Assurance & Retention

Give clients confidence in your security practices while strengthening long-term relationships and retention.

ABOUT SOC 2

Understand SOC 2.

Build Trust. Drive Growth.

SOC 2 - Type 1

SOC 2 Type 1 is an initial stage of compliance within the Service Organization Control framework. It involves a thorough examination of an organization’s systems, policies, and procedures at a specific point in time. The assessment focuses on whether the design of the systems and controls is suitable to meet the criteria for security, availability, processing integrity, confidentiality, and privacy, as defined by the SOC 2 framework.

SOC 2 - Type 2

SOC 2 Type 2 is an advanced level of compliance within the Service Organization Control framework. It involves a comprehensive assessment that not only evaluates the design of an organization’s systems, policies, and procedures but also examines their operational effectiveness over an extended period, typically spanning a minimum of six months. The assessment focuses on criteria for security, availability, processing integrity, confidentiality, and privacy, as outlined by the SOC 2 framework. SOC 2 Type 2 provides a deeper understanding of how well an organization’s controls are implemented and sustained over time, offering stakeholders assurance about the ongoing effectiveness of security measures.

SOC 2- Compliance Consultancy

Our SOC 2 compliance consultancy involves a thorough audit conducted by our expert cyber security consultant. We conduct audit which evaluates an organization’s systems, policies, and procedures against the predefined SOC 2 criteria. The goal is to ensure that the service provider has implemented effective controls to protect client data and maintain the security and privacy of the services they provide.

SOC 2 Report Attestation by AICPA

We get your SOC 2 report attestation by our onboard CPA licensed by AICPA (American Institute of CPAs) involves an independent examination of a service organization’s controls over security, availability, processing integrity, confidentiality, and privacy.

PHASE-1

SOC 2 Implementation

Pre-Assessment

The organization and the auditing firm collaborate to determine the scope, objectives, and timeline of the audit. The auditors gain an understanding of the organization's systems and controls.

01

Risk Assessment

Identification and evaluation of potential risks and vulnerabilities in the organization's systems and processes, helping to shape the audit focus.

02

Control Evaluation

The auditors assess the design and implementation of controls in place to ensure they align with the SOC 2 criteria. This involves examining policies, procedures, and system architecture.

03

Testing and Verification

Operational effectiveness of controls is evaluated over a specified period (for Type 2 audits). This may involve sample testing, interviews, and documentation reviews to ensure controls are consistently applied.

04

Report Generation

After completion of the audit, the auditing firm provides a detailed report summarizing the findings. In the case of SOC 2 Type 1, this report reflects a point-in-time assessment, while SOC 2 Type 2 reports cover a more extended evaluation period.

05

Remediation (if necessary)

If any deficiencies or non-compliance issues are identified, the organization may need to address and remediate these concerns before achieving or maintaining SOC 2 compliance.

06
(Attestation by )

PHASE-2

Attestation Journey

Engagement

We have an onboard qualified CPA (Certified Public Accountant) firm to conduct the SOC 2 attestation. The scope, objectives, and criteria for the audit are defined, and a formal engagement letter is established.

01

Pre-Assessment

We collaborate to understand processes, identify key controls, and determine audit scope. This involves assessing risks, defining control objectives, and establishing the timeframe for attestation.

02

Control Testing

Our CPA firm assesses the design and operating effectiveness of the service organization's controls. This may involve document reviews, interviews, observations, and testing of control activities.

03

Evidence Gathering

The auditors collect and analyze evidence to support their findings and conclusions. This evidence may include policies, procedures, system configurations, and other relevant documentation.

04

Audit Procedures

Our CPA firm performs audit procedures to ensure that the controls are designed and implemented effectively, providing reasonable assurance that they meet the criteria specified in the SOC 2 framework.

05

Report Generation

The CPA firm issues a SOC 2 report. For Type 1 reports, this provides an opinion on control design suitability at a specific point in time. For Type 2 reports, it includes an opinion on control operating effectiveness over a specified period.

06

Opinion & Assurance

The SOC 2 report includes a CPA firm's opinion on the service organization's adherence to SOC 2 criteria, providing assurance to stakeholders such as customers and business partners.

07

Remediation

If any deficiencies or areas of non-compliance are identified, the service organization may need to address and remediate these issues before the final report is issued.

08

Ready To Achieve SOC 2 Compliance?

Let us help you build trust, strengthen security and grow your business.

Why Choose Us?

We are the best SOC 2 implementation

and attestation provider Globally.

With highly skilled and expert team of Cyber security consultants, we make your company reputable in the market

24/7 service available

Highly Qualified Consultants

Improves Quality of your products and Services

Get Certified to qualify for global contracts

SOC 2, ISO 27001, ISO 9001 and many more

Fast and Hazzle Free Process

Testimonials

What Our Clients Say About Us?

Excellent services for our company’s SOC 2 compliance and attestation. We rely only on this company for the last 2 years.

William Banham PFANGE GOUVERNEUR LLC, IL, USA

Over the last 2 years, team SOC 2 has delivered the phenomenal services towards maintaining our compliance and attestation.

Angela Barbour ANGIE’S ROSE GARDEN LLC, NY, USA

Team SOC 2 is Highly Recommended. We rely on them from last 3 years and their delivery of services are extra-ordinary.

Ashu Puri ARIAN MEDICAL LTD, UNITED KINGDOM

Ready to Strengthen Your Compliance?

Take the next step toward stronger security, greater customer trust, and a more efficient compliance process.


Let's discuss your SOC 2 requirements and create a clear path toward compliance.

Latest Posts & News

Stay informed with the latest insights, updates, and expert guidance on SOC 2 compliance, cybersecurity, data protection, and industry standards. Explore our latest articles to better understand compliance requirements and strengthen your organization’s security posture.

Common Challenges in SOC 1 and SOC 2 Compliance and How Expert Providers Help Overcome Them

Common Challenges in SOC 1 and SOC…

Most Recent Posts September 2, 2026 Common Challenges in SOC…
A Complete Guide to VAPT Testing: Process, Methodology, and Benefits 

A Complete Guide to VAPT Testing: Process,…

Most Recent Posts September 2, 2026 A Complete Guide to…
Top Benefits of SOC 2 Compliance Attestation for Growing Businesses

Top Benefits of SOC 2 Compliance Attestation…

Most Recent Posts September 2, 2026 Top Benefits of SOC…